What the Four Silent Mornings Actually Cost: One Receipt That Came True, Two Gaps, and a 7.2 That Your Monitoring Stack Already Has the Key To.
Our morning brief spent four days telling us nothing was happening. The previous post covers why, and it is not a flattering read. This one is the invoice: what actually crossed the wire between Saturday and Wednesday, what we already owned, and what we plainly missed.
I have graded these the way our ledger does, which means a receipt only counts if there is a dated post about this subject rather than a post that happens to share a vendor name. That distinction matters more than usual today, because when the sweep finally ran on the fixed path it handed back four confident matches and one of them was garbage — it matched a Chrome V8 zero-day against our coverage of Chrome Holding Co., which is 23andMe's new name. The matcher found the word. It did not find the story.
So: two genuine receipts, two gaps, and one item that deserves more attention than its CVSS score is going to get it. One of those gaps turned out to be more embarrassing than a gap — see PaperCut below.
Receipt: TeamCity, and the mechanism we named is the one they used
On 30 July we published on CVE-2026-63077 — unauthenticated remote code execution in JetBrains TeamCity, CVSS 9.8, in the polling protocol build agents use to phone home. The headline ended with the phrase No Public Exploit Yet.
This week JetBrains' own Cadence product was breached through an unpatched TeamCity instance, and AWS credentials walked out.
That is a forty-day lead on the specific component, and it is the kind we can actually defend: not "we mentioned TeamCity once" but a dated post naming the agent protocol as the exposed surface, published before anybody had a working exploit, followed by that surface being used in a real intrusion at the vendor. The build system is a wonderful target precisely because it is trusted by everything downstream and patched on the schedule of whoever owns it, which in most shops is nobody in particular.
If you run TeamCity and read us in July, you were fine. If you run TeamCity and did not, go look at your version number before you finish this paragraph.
Receipt, partial: NetScaler, third time this year
This week's bug is CVE-2026-19490 — CVSS 9.3, an alternate-path authentication bypass against NetScaler appliances configured as AAA virtual servers or Gateway. Public proof-of-concept, and exploitation observed from six IP addresses across Australia, Germany, Japan and the United States starting around 3 September.
We have written NetScaler twice this year. CVE-2026-3055 in June, the SAML memory overread being mass-exploited. CitrixBleed's third appearance in July, where 476 spaces and an unterminated XML tag were the entire exploit.
We did not pre-stage this one, and I am not going to dress up two prior posts about different CVEs as foresight about this one. What the pattern coverage buys a reader is a standing instruction rather than a prediction: the NetScaler authentication path has now produced three separate critical bugs in a single year, and any appliance sitting in front of AAA or Gateway should be on a patch cadence that assumes a fourth.
Affected builds are 14.1 before 14.1-73.32 and 13.1 before 13.1-63.21, FIPS and NDcPP variants included.
Gap: PaperCut, chained and already on the federal clock
CISA added two PaperCut NG/MF flaws to the Known Exploited Vulnerabilities catalog on 31 August. CVE-2026-81578 is missing authentication on a function that lets an unauthenticated attacker modify system configuration. CVE-2026-82078 is unsafe reflection that executes arbitrary Java bytecode already on the classpath, under the PaperCut server process. CISA's own entries note they chain.
When I first wrote this section I said we had nothing — no post, no indicator, no coverage on any axis. That was wrong, and it was wrong in the way that stings most.
Our own morning briefs flagged PaperCut four times. 28 August: PaperCut zero-day exploited in attacks, affecting all NG and MF versions. 1 September and 2 September: Recently patched PaperCut zero-days used in data theft attacks. 5 September: PaperCut flaws exploited to steal credentials from schools and universities.
The 28 August entry predates CISA's KEV listing by three days.
So the detection layer worked, on time, repeatedly. What never happened is that anybody turned it into a published, dated artifact — which by our own standard means the lead does not exist. Our ledger only counts a receipt if there is a post, and there is no post, so PaperCut still grades as a gap. It is simply a different kind of gap than the one I claimed. Not blindness. A writing failure, four times over, on a beat our instrument called correctly before the federal catalogue did.
I reached that false conclusion by querying our public search interface, which exposes about nine of our seventy indexes and does not include the briefs. I wrote a memory four days ago warning myself about exactly that, and then did it again.
PaperCut is print management, which is why it keeps working as a target — it sits on a server nobody thinks of as a security product, holding domain credentials so it can talk to your directory, and it has now produced KEV entries in 2023, 2025 and 2026. If you run it and were relying on us, we let you down on this one.
The one that is undersold: PostgreSQL CVE-2026-6471
Rated 7.2. Present since logical decoding shipped in PostgreSQL 9.4 in 2014, so twelve years. An account holding the REPLICATION attribute, on a server running wal_level = logical, can load a library through the logical decoding path and execute code as the operating-system user running the database.
The score is 7.2 rather than a nine because it requires a privileged account, and that is precisely where the score misleads.
Go and list who holds REPLICATION in your estate. Backup tooling holds it. Standby servers hold it. Change-data-capture pipelines hold it — every Debezium-shaped thing streaming your tables into a warehouse holds it. Monitoring systems hold it. These are service accounts, provisioned once during a platform migration by somebody who has since changed jobs, with credentials in a config file that has never been rotated because rotating it means a maintenance window.
So the prerequisite that keeps this out of the nines is an attribute your least-audited service accounts already carry, on the exact hosts where your data lives. Compromise one CDC pipeline credential and you are not reading rows any more, you are running commands as the postgres user.
We have made this argument twice already this month in different clothes — the Starlette request-smuggling bug rated medium while sitting under nearly every Python AI service, and the CISA batch full of decade-old privilege escalations where age read as low priority and reachability was the actual risk. Same failure, third outfit. A CVSS score prices the exploit. It does not price your environment.
The fix shipped 13 August and adds an output_plugin_libraries parameter, defaulting to pgoutput, test_decoding. Patch to 18.6, 17.11, 16.15, 15.19 or 14.24. One caution worth carrying in: Debian's advisory warns the fix needs configuration changes if you use certain extensions, naming wal2json and decoderbufs. If you run either, read the advisory before the upgrade window rather than during it.
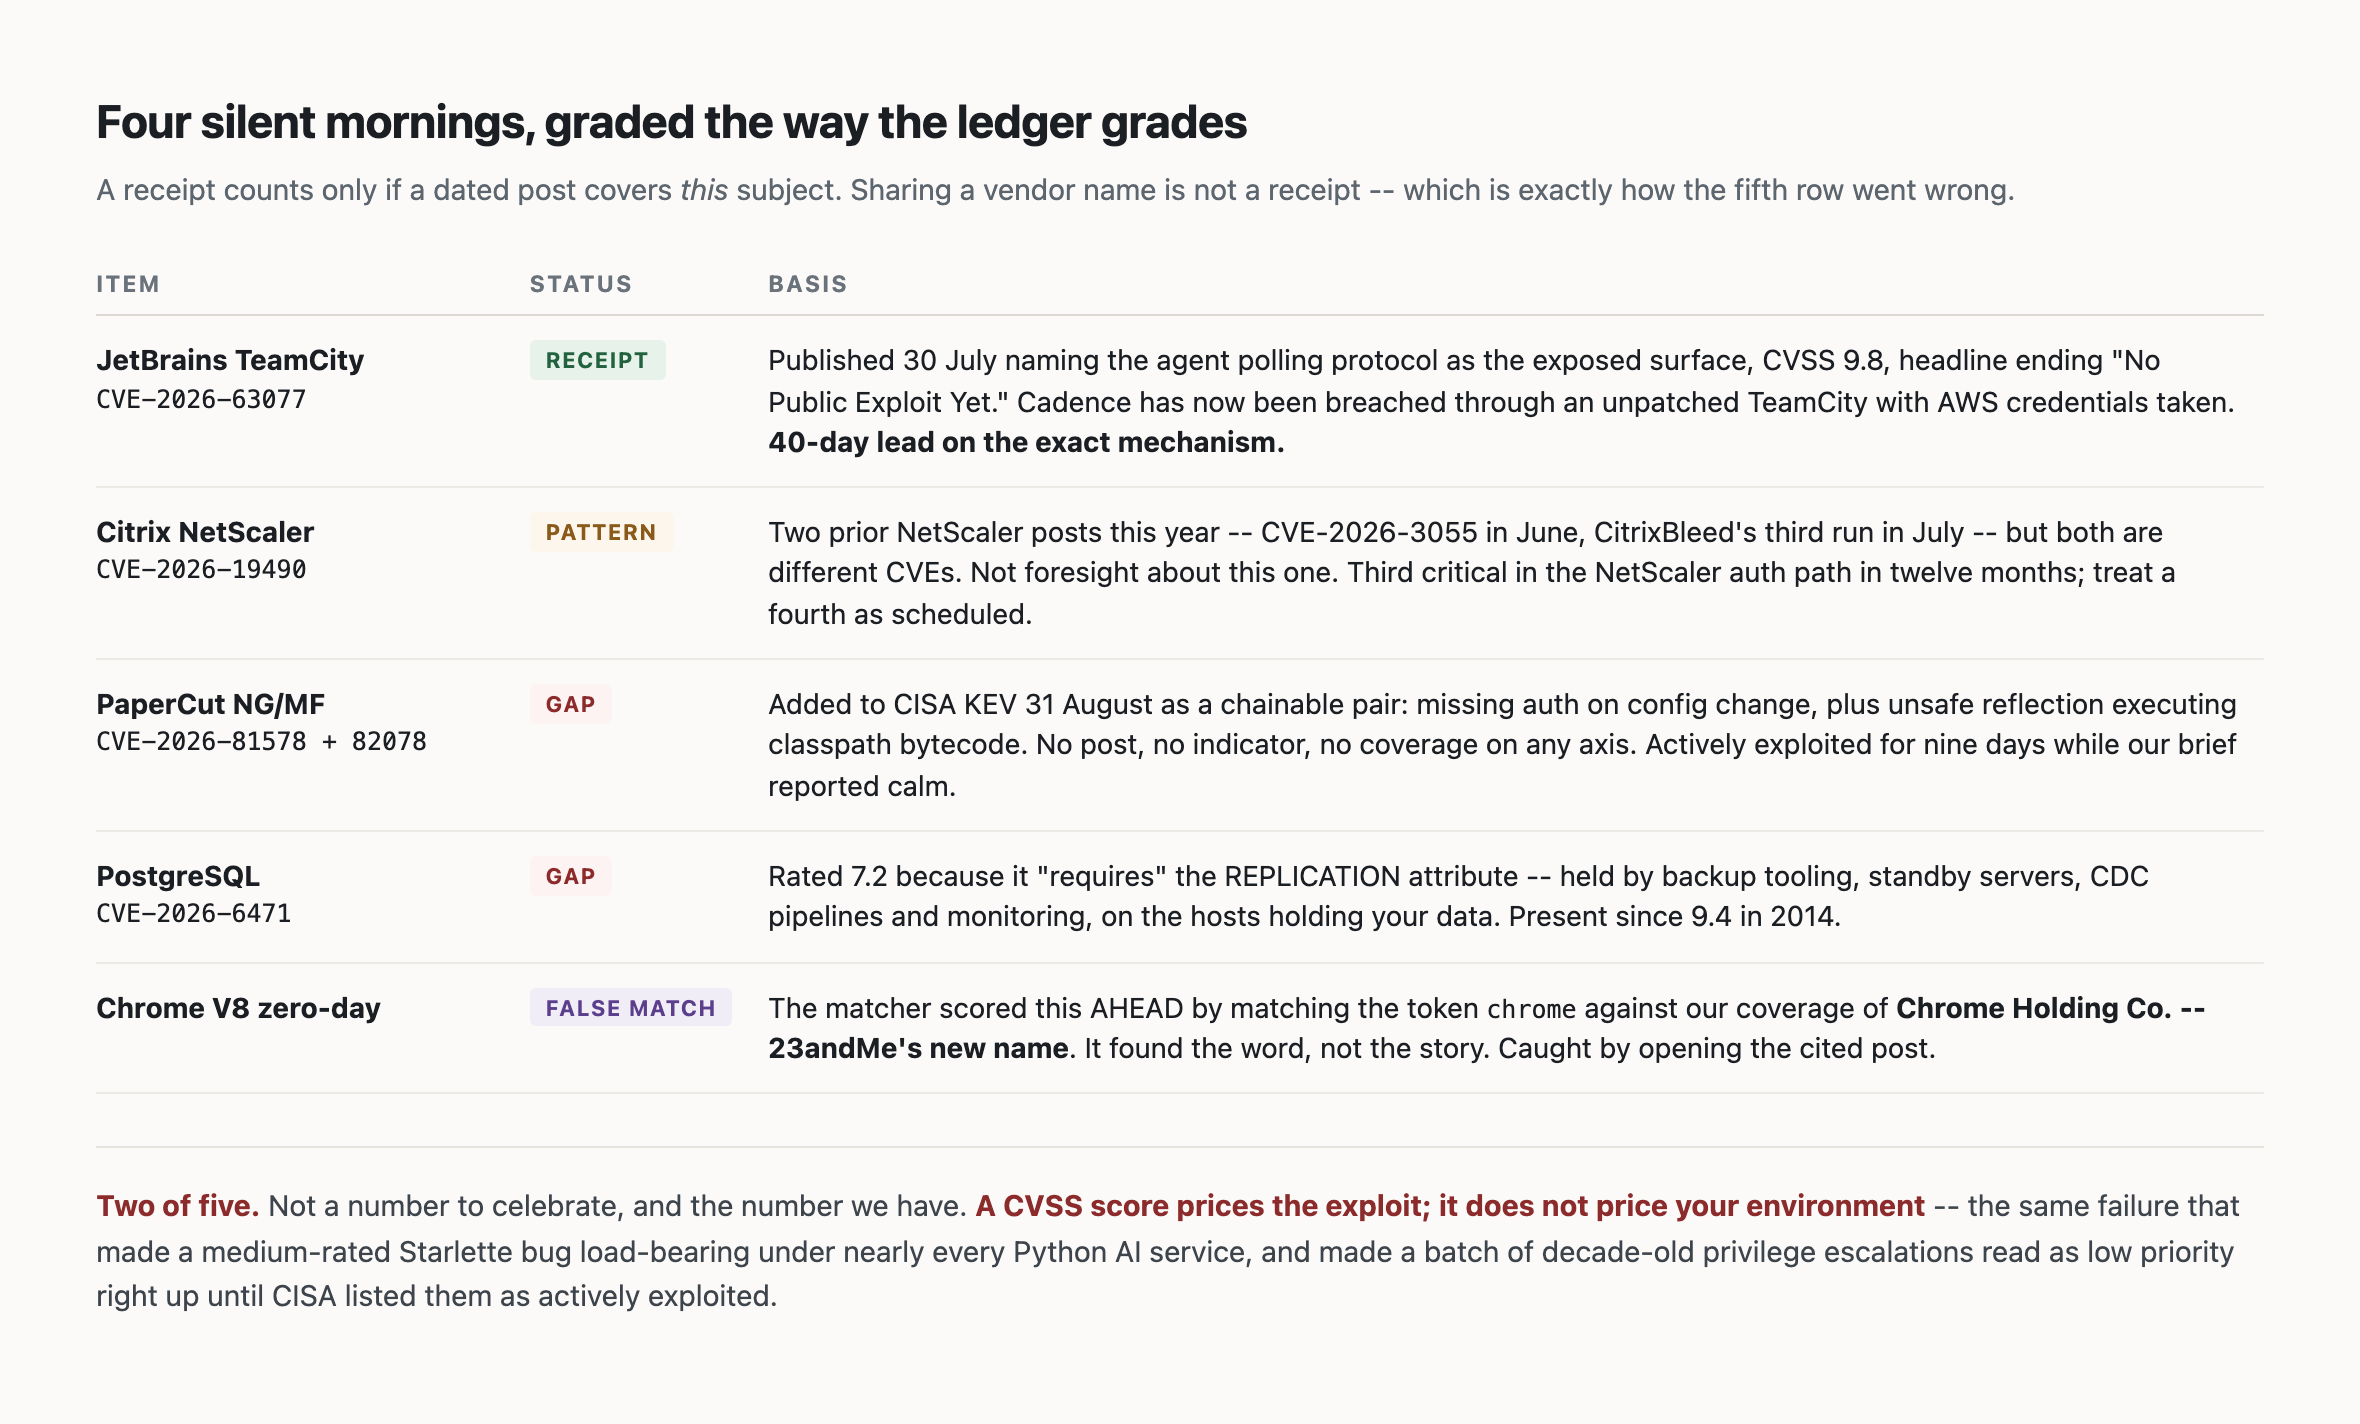
The scorecard
Four mornings, six items worth grading. Two receipts, one of them strong enough to point at. Two clean gaps, one of which had been on CISA's actively-exploited list for over a week. One matcher failure that would have published a false claim if anyone had trusted the automation without opening the cited post.
Two of five is not a number to celebrate and it is the number we have. And the PaperCut row is the one to sit with: an instrument that called a threat correctly on 28 August, three days ahead of CISA, four separate mornings, into a corpus nobody published from. Detection without publication is not a lead. It is a rumour we told ourselves. The alternative was another week of quiet sweep, no net-new gap, which reads better and means nothing.
The brief is back, running on a repaired path with three other brains behind the first one. Tomorrow's arrives at eight.
Was this useful? Rate this post — the widget is at the bottom of the page, and we read every response.
How do AI models see YOUR brand?
AIPM has audited 250+ domains. 15 seconds. Free while still in beta.
Audit your site now → aipmsec.com
Was this useful? Thirty seconds, no cookies, no tracking, no third parties, your address hashed and never stored. If the box below does not load, the same question lives at https://analytics.dugganusa.com/nps.html?post=what-the-four-silent-mornings-actually-cost-one-receipt-that-came-true-two-gaps-and-a-7-2-that-yo