UnrealIRCd CVE-2026-114713 Is on CISA's Exploited List, Due Monday: Any User on a Linked Network Can Speak as a Server
If you run an UnrealIRCd network with two or more linked servers, upgrade every server to 6.2.7.1, or apply the hot-patch, before Monday, November 16. CISA added CVE-2026-114713 to its Known Exploited Vulnerabilities catalog today, Friday, November 13, 2026, and gave federal agencies three days. CISA also flagged it for forensic triage, so after you patch, look back through your logs for kills, bans, operator changes and server links that nobody on your staff issued.
What CISA says, from the KEV JSON
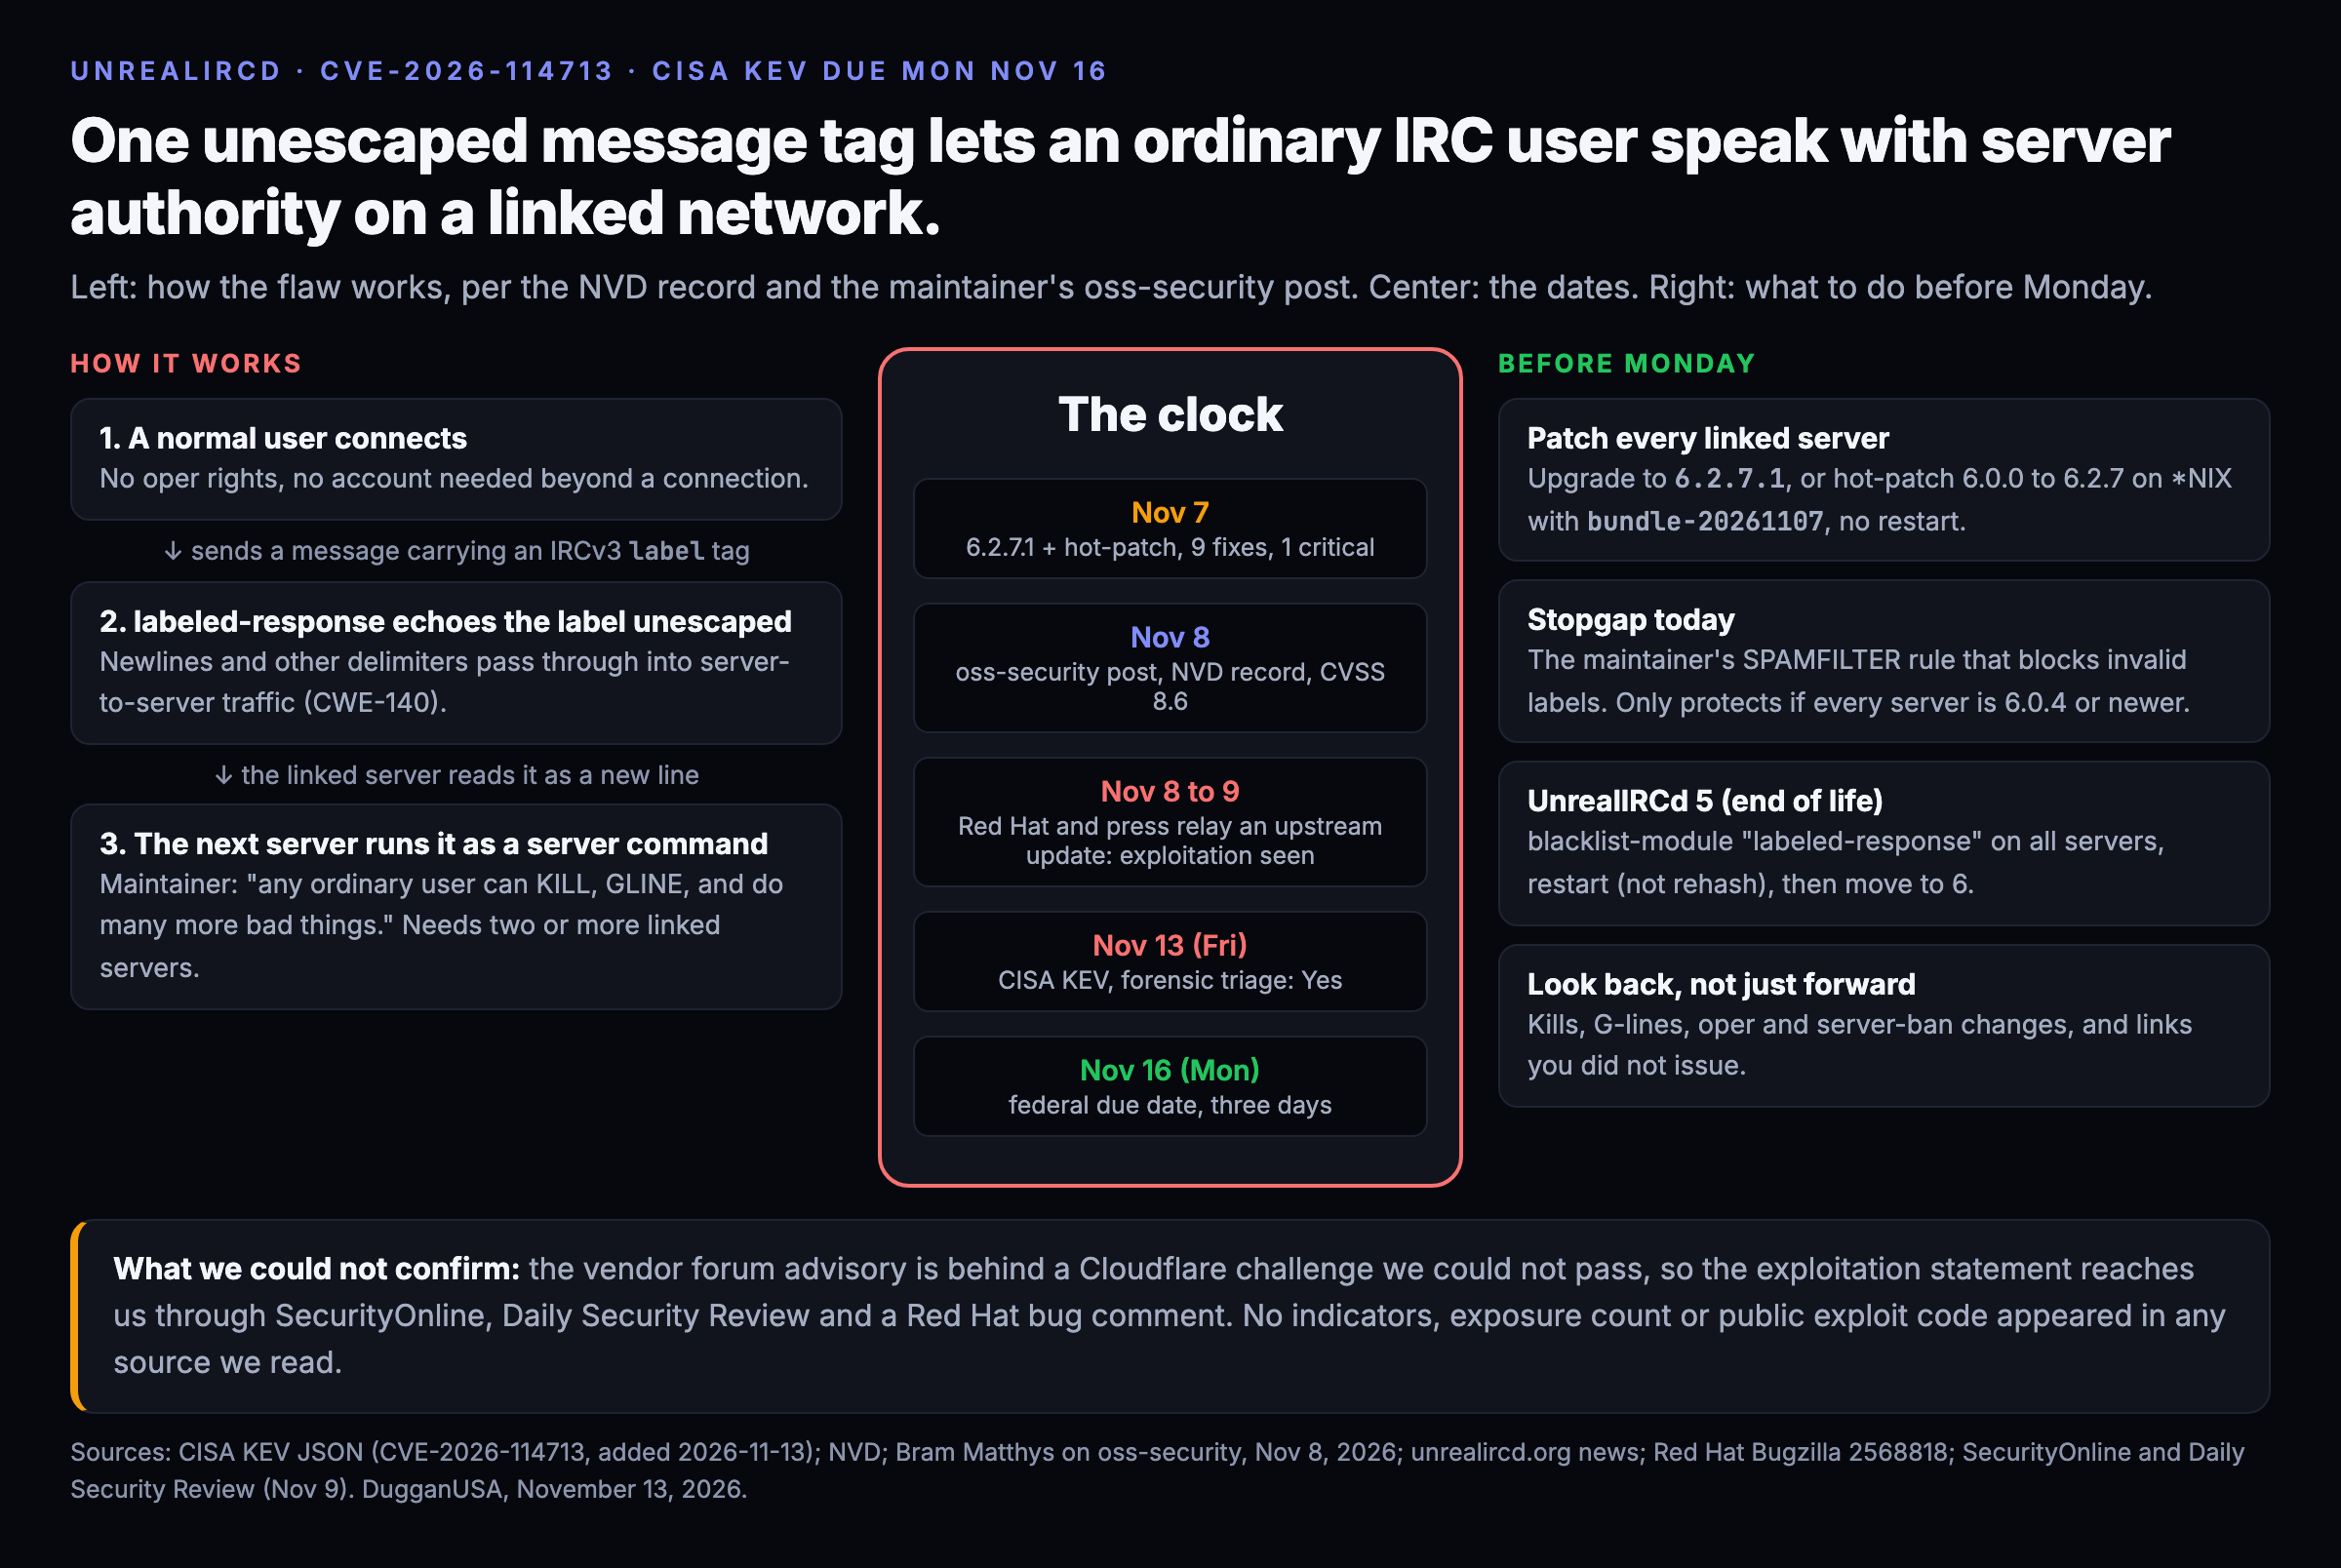
We read the entry directly from CISA's catalog feed. It was added 2026-11-13 with a due date of 2026-11-16. The weakness is CWE-140, improper neutralization of delimiters. CISA's description: the flaw "allows any user on a network with two or more linked servers to inject server-to-server commands that are executed with server authority." Ransomware campaign use is listed as "Unknown". The forensic triage flag is "Yes", and the required action points to BOD 26-04 and its forensics triage requirements.
What that flag asks, in one sentence from CISA's BOD 26-04 implementation guidance: before patching or containment, collect volatile evidence, analyze it for signs of compromise, write a triage report, and report any confirmed compromise to CISA. The due date binds U.S. federal agencies; everyone else can treat the flag as advice that patching alone does not tell you whether someone already got in.
What the flaw is
The NVD record, published November 8, says: "The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 'label' message tag when echoing it into replies." IRC is a line-based text protocol. If a user can put a line break into a label, the reply that one server passes to the next carries an extra line, and the receiving server treats that line as a command from a server. The NVD record carries a CVSS 3.1 score of 8.6 from MITRE, with no privileges or user interaction required.
UnrealIRCd's maintainer, Bram Matthys (Syzop), wrote on the oss-security list on November 8 that "any ordinary user can KILL, GLINE, and do many more bad things." The project's news page called it a critical issue that "allows normal users to execute commands with server/IRCOp authority."
The condition matters: CISA and NVD both say a network needs two or more linked servers. Neither source we read discusses single-server deployments directly, so we read that wording as saying a lone, unlinked server is outside this flaw. It is still one of nine issues fixed in the same release, so patch it anyway.
Versions and fixes
- Fixed: UnrealIRCd 6.2.7.1, released Saturday, November 7, 2026. The release fixes nine security issues, one rated critical.
- Affected: 6.0.0 through 6.2.7, per NVD and the maintainer.
- Hot-patch: on Unix-like systems, running the unrealircd script with hot-patch bundle-20261107 patches 6.0.0 to 6.2.7 in place with no restart. The maintainer says to confirm afterwards with the module-status command, filtered for labeled-response. Windows servers are not covered by the hot-patch; upgrade them.
- Stopgap you can apply in minutes: the maintainer posted a SPAMFILTER rule, added by an IRC operator, that blocks malformed labels network-wide. He says it protects against the critical issue only if every linked server runs 6.0.4 or newer. The exact rule is in his oss-security post; copy it from there rather than from a news site.
- UnrealIRCd 5 (end of life since July 1, 2023): the maintainer says it is affected too. His advice is to add a blacklist-module line for "labeled-response" to the configuration on every server and restart (a rehash is not enough), then move to version 6. Older versions were not checked; he believes several of the bugs go back to 3.2.x.
Was it exploited, and how do we know
CISA lists it as known exploited. NVD also carries CISA's assessment marking exploitation as active and the flaw as automatable.
The vendor side is less direct, and we want to be clear about it. The maintainer's oss-security post of November 8 does not say exploitation was seen. Two press articles dated November 9 (SecurityOnline and Daily Security Review) quote an update added to the vendor's forum advisory: "We are seeing bad guys exploiting this issue on the internet right now." A Red Hat Bugzilla comment of November 8, 19:13 UTC says "Upstream reports active exploitation attempts." We could not read the forum advisory ourselves: forums.unrealircd.org returned a Cloudflare challenge (HTTP 403) to every request we made. Those three secondary sources agree, but all of them point back to that one forum post.
No source we read names who is exploiting it, what they did after, or how many networks were hit.
Who is exposed
- Community IRC networks. Volunteer-run networks are the classic UnrealIRCd deployment and are usually linked across several servers. These are the operators least likely to read CISA's catalog.
- Organizations that run IRC internally. Some companies and open-source projects still run linked IRC for operations chat or bots.
- Federal and contractor systems, which are who the three-day deadline formally applies to.
- Attacker infrastructure. IRC servers have long been a common command channel for botnets. That means some vulnerable UnrealIRCd instances are not victims in the usual sense. We draw no conclusion from that about who is exploiting this flaw; the sources we read do not say.
We found no exposure count. None of the sources we read gave a Shodan or Censys figure, and Daily Security Review reports that the project has not published the number of affected networks. We did not run our own scan.
Public exploit code
We searched GitHub repository names for the CVE number and for UnrealIRCd plus label, and our own corpus for the CVE. We found no proof-of-concept repository and no harvested exploit fingerprints. That reflects what our searches cover, not proof that none exists; the mechanism is simple enough that anyone reading the fix could build one.
What to look for if you were exposed
These are our suggestions, built from what the maintainer says an attacker can do. Neither UnrealIRCd nor CISA has published indicators.
- Kills, G-lines, Z-lines, shuns and other network bans that appear to come from a server rather than from a named operator, especially ones none of your operators remember issuing.
- Changes to operator status, user modes, spamfilters or server-side bans you did not make.
- Server links, squits or link attempts you did not plan.
- Clients that sent messages with unusually long or malformed label tags, if you log message tags. Keep the logs before you rotate them; the forensic triage flag is about evidence, and rotation destroys it.
- If you find any of the above, treat the network's operator accounts and link passwords as exposed and rotate them after patching.
Our edge sees web traffic, not IRC
Our edge instruments see HTTP requests, not IRC on ports 6667 or 6697, so we have no telemetry on this flaw and make no claim either way. No indicators were published in the sources we read, so we add none to our feed. We make no claim to have seen this first.
Sources
- CISA Known Exploited Vulnerabilities catalog, JSON feed, entry CVE-2026-114713, added 2026-11-13, due 2026-11-16
- CISA BOD 26-04 implementation guidance, forensic triage steps: https://www.cisa.gov/news-events/directives/bod-26-04-implementation-guidance-prioritizing-security-updates-based-risk
- NVD, CVE-2026-114713: https://nvd.nist.gov/vuln/detail/CVE-2026-114713
- Bram Matthys, "UnrealIRCd 6.2.7.1 released & hot-patch (CVE-2026-114713)", oss-security, November 8, 2026: https://www.openwall.com/lists/oss-security/2026/11/08/1
- UnrealIRCd news page: https://www.unrealircd.org/index/news
- UnrealIRCd forum advisory (could not be read, Cloudflare challenge): https://forums.unrealircd.org/viewtopic.php?t=9487
- Red Hat Bugzilla 2568818: https://bugzilla.redhat.com/show_bug.cgi?id=2568818
- SecurityOnline, November 9, 2026: https://securityonline.info/unrealircd-vulnerability-cve-2026-114713-exploited/
- Daily Security Review, November 9, 2026: https://dailysecurityreview.com/?p=45510
Every indicator in this post is in the feed. Free.
1.58M+ IOCs, STIX 2.1 / TAXII, 88% novel vs ThreatFox, exploited-CVE leads ahead of CISA. No credit card — a free API key in 30 seconds, and you can audit every claim above against the live endpoints.