A Public iOS Sandbox Escape Lets One App Read Other Apps' Files on iOS 26 and 27, and Apple Has Confirmed No Fix. Binance Says Keep Wallet Secrets Away From Sideloaded Apps. Here Is What That Means
If you keep a crypto wallet, a password manager or any app with sensitive data on an iPhone, and the same phone also has apps installed outside the App Store (through AltStore, SideStore or a manually signed build), remove the outside-store apps today. A researcher who goes by forcequit published code on November 8 for a sandbox escape called worse_query that lets an app read other apps' data folders on iOS 26 and 27. Apple's iOS 27.2.1 and 26.7.3 updates, released the next day, do not mention it, and no fix has been confirmed. Binance published a warning. Neither Binance nor the researcher reports any theft.
What has been reported
The primary sources are the researcher's public repository, Binance's security warning, and Apple's two security-note pages. The Hacker News (Swati Khandelwal, November 10) is our route to the Binance and Apple details, so those two are second-hand to us.
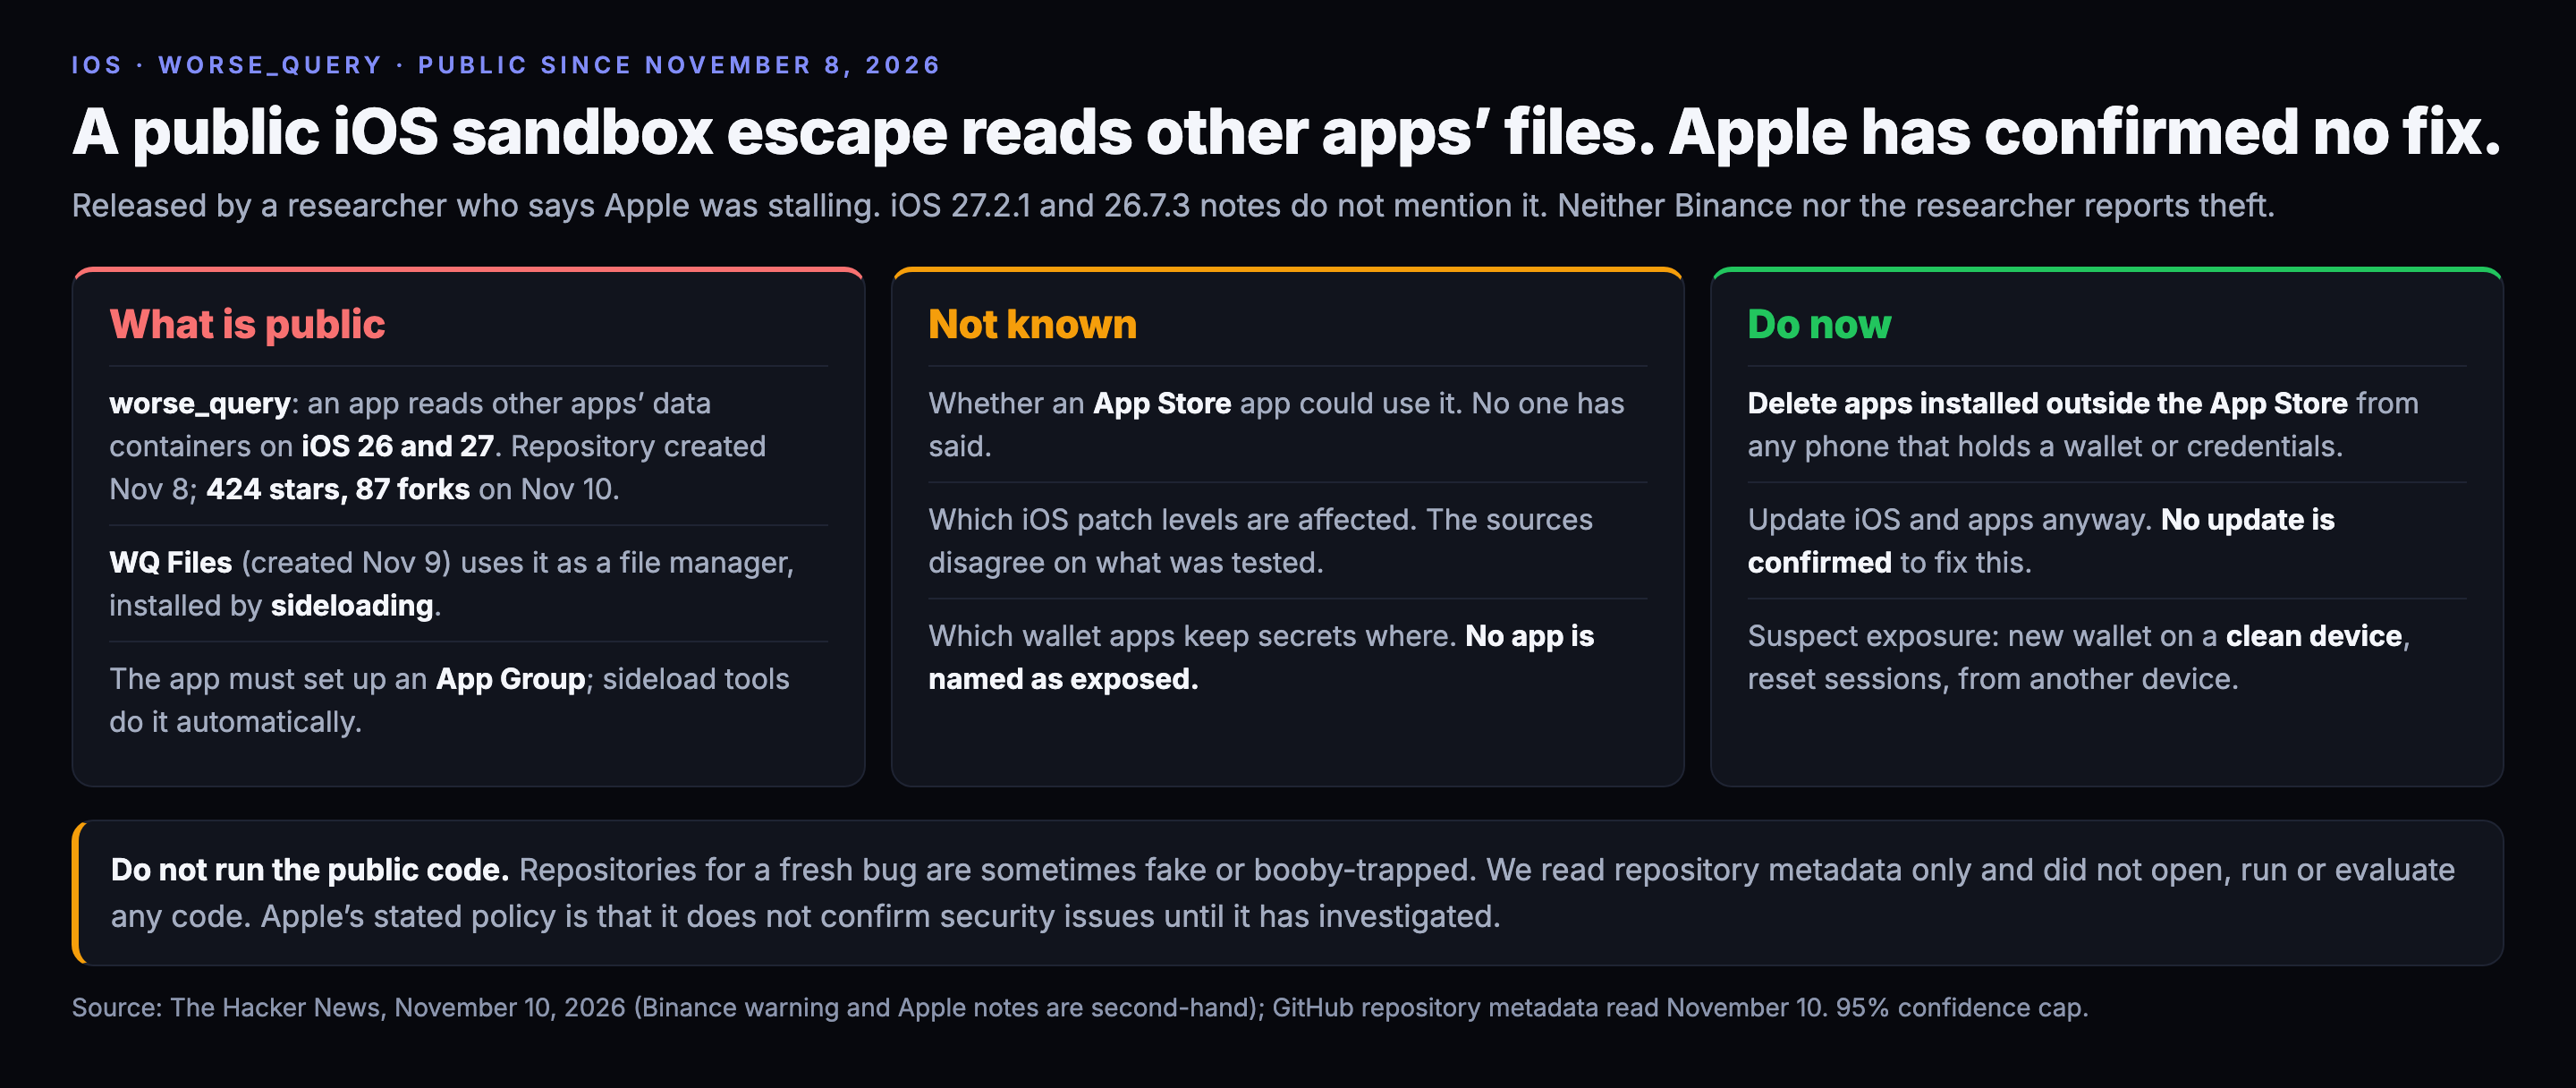
- The exploit: the repository, created November 8 with the description "A sandbox escape for iOS 26 and 27, again," had 424 stars and 87 forks when we read its metadata on November 10. We did not open or run the code. The Hacker News says it can reach every app's data container on an iPhone, and some system folders on iOS 27, and that an app must set up an App Group container to use it.
- How it got out: the researcher is quoted by The Hacker News saying he "had not planned to release worse_query early" and that "Apple was stalling on responding to me and people started larping with it on here." The report does not say the release was coordinated with Apple.
- A tool built on it: a developer published WQ Files, a file manager that reaches other apps' data without a jailbreak or a kernel exploit and can edit, delete and clear it. Its repository was created November 9. It installs through sideloading tools, which create the App Group automatically with an Apple ID. Another project's README now says iOS 27.2.1 is "pretty sure" supported.
- Apple: its iOS 27.2.1 and 26.7.3 security notes, as The Hacker News reports them, do not mention worse_query or any sandbox issue. Apple's stated policy, quoted there: it "does not disclose, discuss, or confirm security issues until it has investigated." No CVE has been reported.
- Binance: warns that the escape puts "seed phrases, private keys, and login credentials" at risk from malicious apps. It names no wallet app as exposed, and neither does the researcher.
What it means, and what it does not
The route in is an app running on the phone. The people who can use this today without any other bug are people who can get an app onto your phone: a sideloaded or manually signed app, which is exactly what WQ Files is. Whether an App Store app could use it is something nobody in the sources we read has said. That uncertainty cuts both ways: we cannot call App Store apps safe, and we have no evidence they are being used this way.
What the data at risk depends on is how each app stores it. An app that keeps secrets in the iOS Keychain is a different case from one that keeps them in its own data folder. The sources do not say which wallet apps use which, so we cannot tell you any particular app is or is not exposed.
What to do
- Delete apps installed outside the App Store from any iPhone that holds wallets or credentials. This is Binance's first piece of advice, and it removes the only confirmed route in.
- Update iOS and your apps anyway. No update is confirmed to fix this, but the same updates fix other flaws, including two iMessage issues and several Bluetooth ones.
- Keep large holdings out of software wallets on a phone you also use to try out outside-store apps. A hardware wallet or a phone that runs only App Store apps removes the route.
- If you have run an unknown sideloaded app on a phone with a wallet, Binance's advice is to move funds to a new wallet created on a clean device and to reset all active login sessions. Do it from a different device.
- Developers and security teams: do not treat the app sandbox as a secrecy boundary for anything you would be unable to rotate. Store secrets in the Keychain with the strictest access class you can, and make sessions revocable server-side.
- Watch Apple's security release notes for the next iOS point release and re-check then. Do not rely on an update note that does not mention this.
What is not known
Whether Apple has a fix coming and when. Which iOS versions are affected beyond "26 and 27," since the sources disagree about exactly which patch levels were tested; The Hacker News notes that none of the sources it lists includes 26.7.3. Whether an App Store app can use it. Whether anyone has used it against real victims: neither the exchange nor the researcher reports any. Which wallets keep secrets where.
How we know, and how we checked
We read The Hacker News report on Binance's warning and read GitHub metadata for the two public repositories (creation and push dates, descriptions, star and fork counts). We did not open, run or evaluate any code, and we did not read Apple's notes or Binance's post directly; those come through The Hacker News. Public code for a fresh bug is sometimes fake or booby-trapped, so do not run it. A search of our corpus found no earlier post of ours on this. We add no indicators to our feed: none are published, and there is no network infrastructure involved.
Sources
The Hacker News, "Binance Warns of iOS Sandbox Escape That Could Expose Crypto Wallet Keys, No Fix Confirmed," November 10, 2026. GitHub repository metadata for worse_query and WQ Files, read November 10, 2026. As cited there and not opened by us: Binance security warning on X; Apple iOS 27.2.1 and 26.7.3 security notes.
How do AI models see YOUR brand?
AIPM has audited 250+ domains. 15 seconds. Free while still in beta.