FortiSIEM 7.5.0 Now Has a Public Exploit That Needs No Login. The Fix Is One Version Up, and Port 27918 Should Never Face the Internet.
FortiSIEM 7.5.0 has a critical flaw, CVE-2026-106173 (CVSS 9.4), that lets anyone who can reach TCP port 27918 run code on the box without logging in. Fortinet fixed it on October 13. On October 20, Horizon3.ai published a working exploit. If you run 7.5.0, upgrade to 7.5.1 or later today. If you cannot, block port 27918 from everything except the hosts that need it. Version 7.6 and FortiSIEM Cloud are not affected.
How the attack works
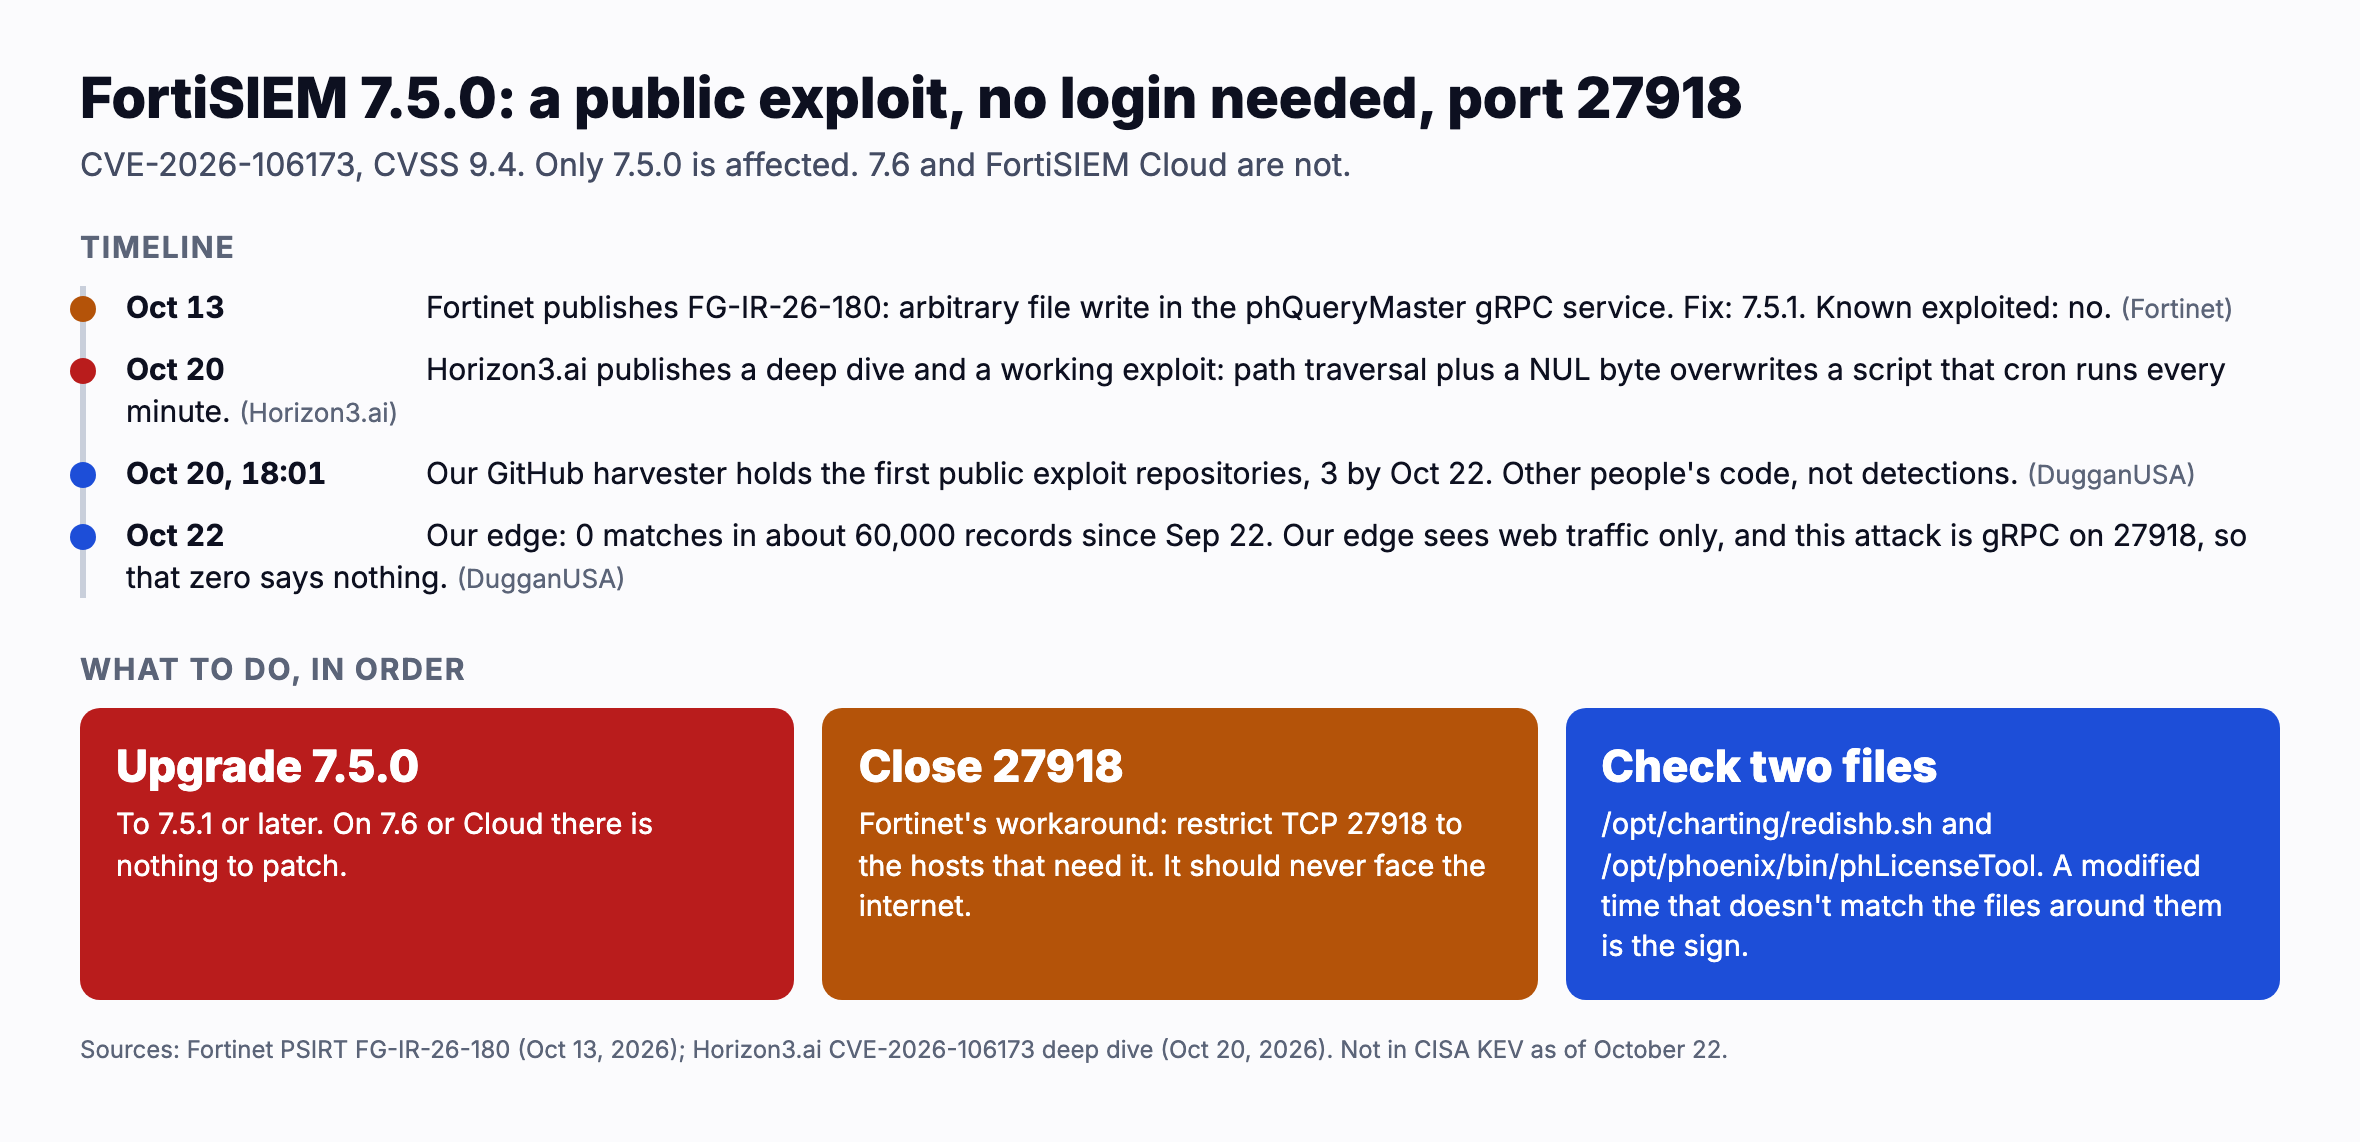
FortiSIEM runs a service called phQueryMaster that listens for gRPC requests on port 27918, on every network interface. It uses TLS but does not ask the caller to prove who they are. One of its functions writes query results to a file whose name is built from a value the caller sends. Horizon3.ai showed that a path like "../" in that value moves the file anywhere on disk, and a NUL byte cuts off the file ending the program adds. Their exploit overwrites a health-check script that cron runs every 60 seconds, so the attacker's code runs within a minute.
What to do, in order
- Upgrade 7.5.0 to 7.5.1 or later. That is the only affected version in Fortinet's advisory.
- Restrict TCP 27918. Fortinet's own workaround. A SIEM's internal query service should never be reachable from the internet, or from most of your network.
- Look for signs it already happened. Horizon3.ai says application logs will not show it. Check /opt/charting/redishb.sh and /opt/phoenix/bin/phLicenseTool, and look for unexpected files named like "result-(IP address)-0-0-(number).dat". A modified time that doesn't match the files around them is the warning sign.
Fortinet lists the flaw as not known to be exploited, and it is not in CISA's Known Exploited Vulnerabilities catalog as of the October 21 edition. A public exploit for a no-login bug in a security product usually shortens that window. CISA has added nine Fortinet flaws to that catalog so far in 2026, the most recent on October 16.
What our instruments can and cannot see
- Our GitHub harvester picked up public exploit repositories for this CVE from 18:01 UTC on October 20, three of them by October 22. That is when we collected other people's code, not a detection. We have not vetted them, so do not run them.
- Our edge found no match for this exploit across about 60,000 blocked requests, decoy hits and origin captures since September 22. That zero means nothing here. Our edge sees web traffic, and this attack is gRPC on port 27918. No web-layer sensor, ours included, will see it.
- Indicators. No IP addresses or domains are tied to this flaw yet, so there is nothing to add to our feed. If attacks start and someone publishes sources, we will add them.
Fortinet's advisory, with the version table and the workaround: Fortinet PSIRT FG-IR-26-180.
If this was useful, or if it wasn't, the rating widget below takes ten seconds and is the only way we know.
Every indicator in this post is in the feed. Free.
1.58M+ IOCs, STIX 2.1 / TAXII, 88% novel vs ThreatFox, exploited-CVE leads ahead of CISA. No credit card — a free API key in 30 seconds, and you can audit every claim above against the live endpoints.
Get your free key → analytics.dugganusa.com/stix/register
Was this useful? Thirty seconds, no cookies, no tracking, no third parties, your address hashed and never stored. If the box below does not load, the same question lives at https://analytics.dugganusa.com/nps.html?post=fortisiem-7-5-0-now-has-a-public-exploit-that-needs-no-login-the-fix-is-one-version-up-and-port-27