Chainalysis Now Says Password Hashes and Live Tokens for All Its Users Were Exposed. KYT Went Offline, and Every User Must Reset and Rotate Before It Comes Back.
If you use Chainalysis, rotate your API keys and change any password you reused on another system. Chainalysis says that names, usernames, password hashes and live tokens for all of its users were exposed to a malicious actor. When your access is restored, you will be forced to reset your password and rotate API keys before you can register transactions. Do not wait for that prompt to rotate keys that other systems hold.
What changed since October 31
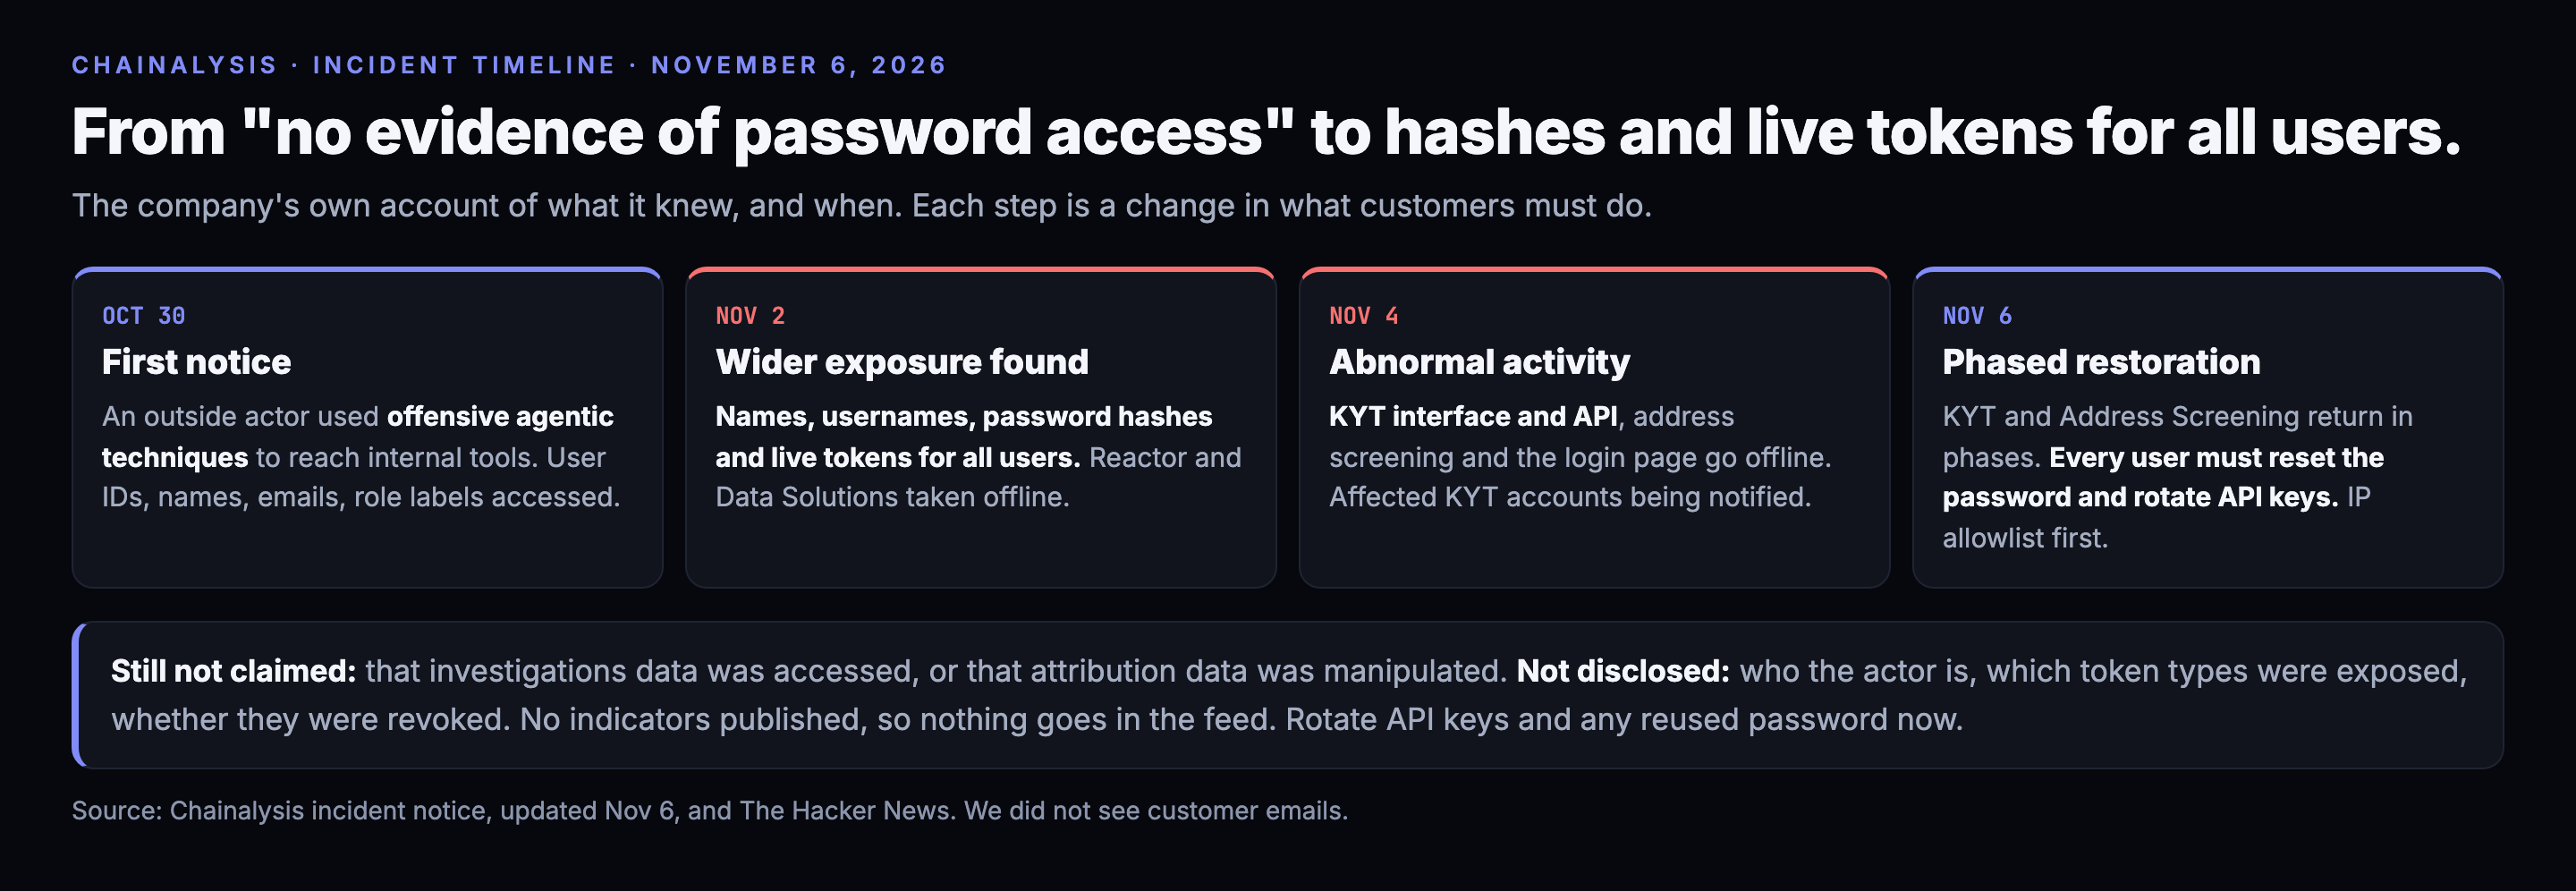
On October 31 we wrote that Chainalysis told customers an outside actor used "offensive agentic techniques" to reach its internal tools, and that the exposed data was user IDs, full names, email addresses and role labels, with no evidence of password access (https://www.dugganusa.com/post/chainalysis-agentic-techniques-breach-what-is-known). That was the company's position that day. It is no longer its position.
According to Chainalysis's incident page, updated November 6, the company discovered on Monday, November 2 that names, usernames, password hashes and live tokens for all Chainalysis users were exposed. While it investigated, it removed access to Reactor and Data Solutions. It says it continues to have no evidence that any investigations data was accessed or that its attribution data was manipulated.
On November 4 it saw abnormal activity in its transaction screening products and took KYT, both the interface and the API, offline, along with other address screening products and the login page. It says it is directly notifying customers whose KYT accounts appear to have been accessed without authorization. The Hacker News, summarizing the notice, also reports an earlier "on-path attack" that exposed a subset of customer passwords and says the vector has been addressed. We did not find that wording in the sections of the notice we read, so treat it as The Hacker News's characterization.
What it means for you
A password hash is not a password, but a stolen hash can be cracked offline, and weak or reused passwords fall first. A live token is the larger problem: depending on what it is, it can let someone act as the user without a password at all. Chainalysis does not say which kinds of token were exposed, how long they live, or whether the company has revoked them. It does say every user must reset passwords and rotate API keys, which implies it considers existing credentials unsafe.
Chainalysis's customers include compliance teams that screen transactions and investigators who trace funds, so account access matters to people other than the customer.
What to do
- Rotate every Chainalysis API key you hold, in every system that calls KYT or Address Screening. Check secrets stores, CI variables and code repositories for old copies.
- Change any password you reused from your Chainalysis account anywhere else, and enable MFA on those accounts.
- Review your account's login and API history for activity you do not recognize, especially for KYT. Chainalysis says it is contacting customers whose KYT accounts appear to have been accessed, but silence is not a clean result.
- Send your trusted IP addresses to Chainalysis support or your account team, as the notice asks, so they can be allowlisted before access returns.
- Expect phishing that uses your name, email address and role. The October exposure already gave an attacker everything needed to write a convincing message. Confirm any reset prompt through the Chainalysis site you typed yourself, not through a link.
The steps other than the allowlist and reset instructions are our reading of the situation. The company's notice gives its own instructions.
Restoration status
At 3:30 a.m. Eastern on November 6, Chainalysis said it had begun restoring KYT and Address Screening in phases, with more customers regaining access over several hours. Reactor and Data Solutions were still being worked on. The Hacker News adds that the activity resembles other recent attacks on technology platforms, naming Chainstack, OpenCode, Warp and WorkOS, and cites Microsoft and Wiz on agentic frameworks that hunt for exposed secrets in public repositories. We covered the Chainstack case here (https://www.dugganusa.com/post/chainstack-breach-node-credentials-exposed). Chainalysis itself says only that its incident is similar to those on other platforms. It has not said who is behind it.
What is not known
Who the actor is, and how they got in. Which token types were exposed and whether they were revoked. How many KYT accounts were accessed. What the "abnormal activity" on November 4 consisted of. Whether the hashes were salted and which algorithm was used. The company publishes no indicators such as IP addresses, domains or file hashes, so there is nothing to put in the feed, and we ingested nothing.
Limits
We read Chainalysis's own incident page as of its November 6 update and The Hacker News's summary of it. We did not see the customer emails. We did not verify any claim independently, and the page changes as the company updates it. Our October 31 post carries a dated note pointing here.
Five percent of this is wrong somewhere. It always is. If you are a Chainalysis customer and have details we lack, tell us.
Was this useful? Rate this post. The widget is at the bottom of the page, and we read every response.
Every indicator in this post is in the feed. Free.
1.58M+ IOCs, STIX 2.1 / TAXII, 88% novel vs ThreatFox, exploited-CVE leads ahead of CISA. No credit card — a free API key in 30 seconds, and you can audit every claim above against the live endpoints.