Command and Control With No Server to Block: A Field Guide to the Five Ways Malware Now Hides Its Orders in Things You Can't Blocklist
For twenty years the basic move in network defense has been the same: find the server the malware talks to, and block it. A command-and-control server has an address, the address goes on a list, and the list goes on your firewall.
This year that move stopped working against a growing share of malware, because the malware stopped having a server worth blocking. This morning's PoeLLM report made it obvious. A botnet of hijacked AI servers learns where its command server is by reading a poem on GitHub. Change a few words in the poem and the whole botnet moves. You cannot put GitHub on a blocklist.
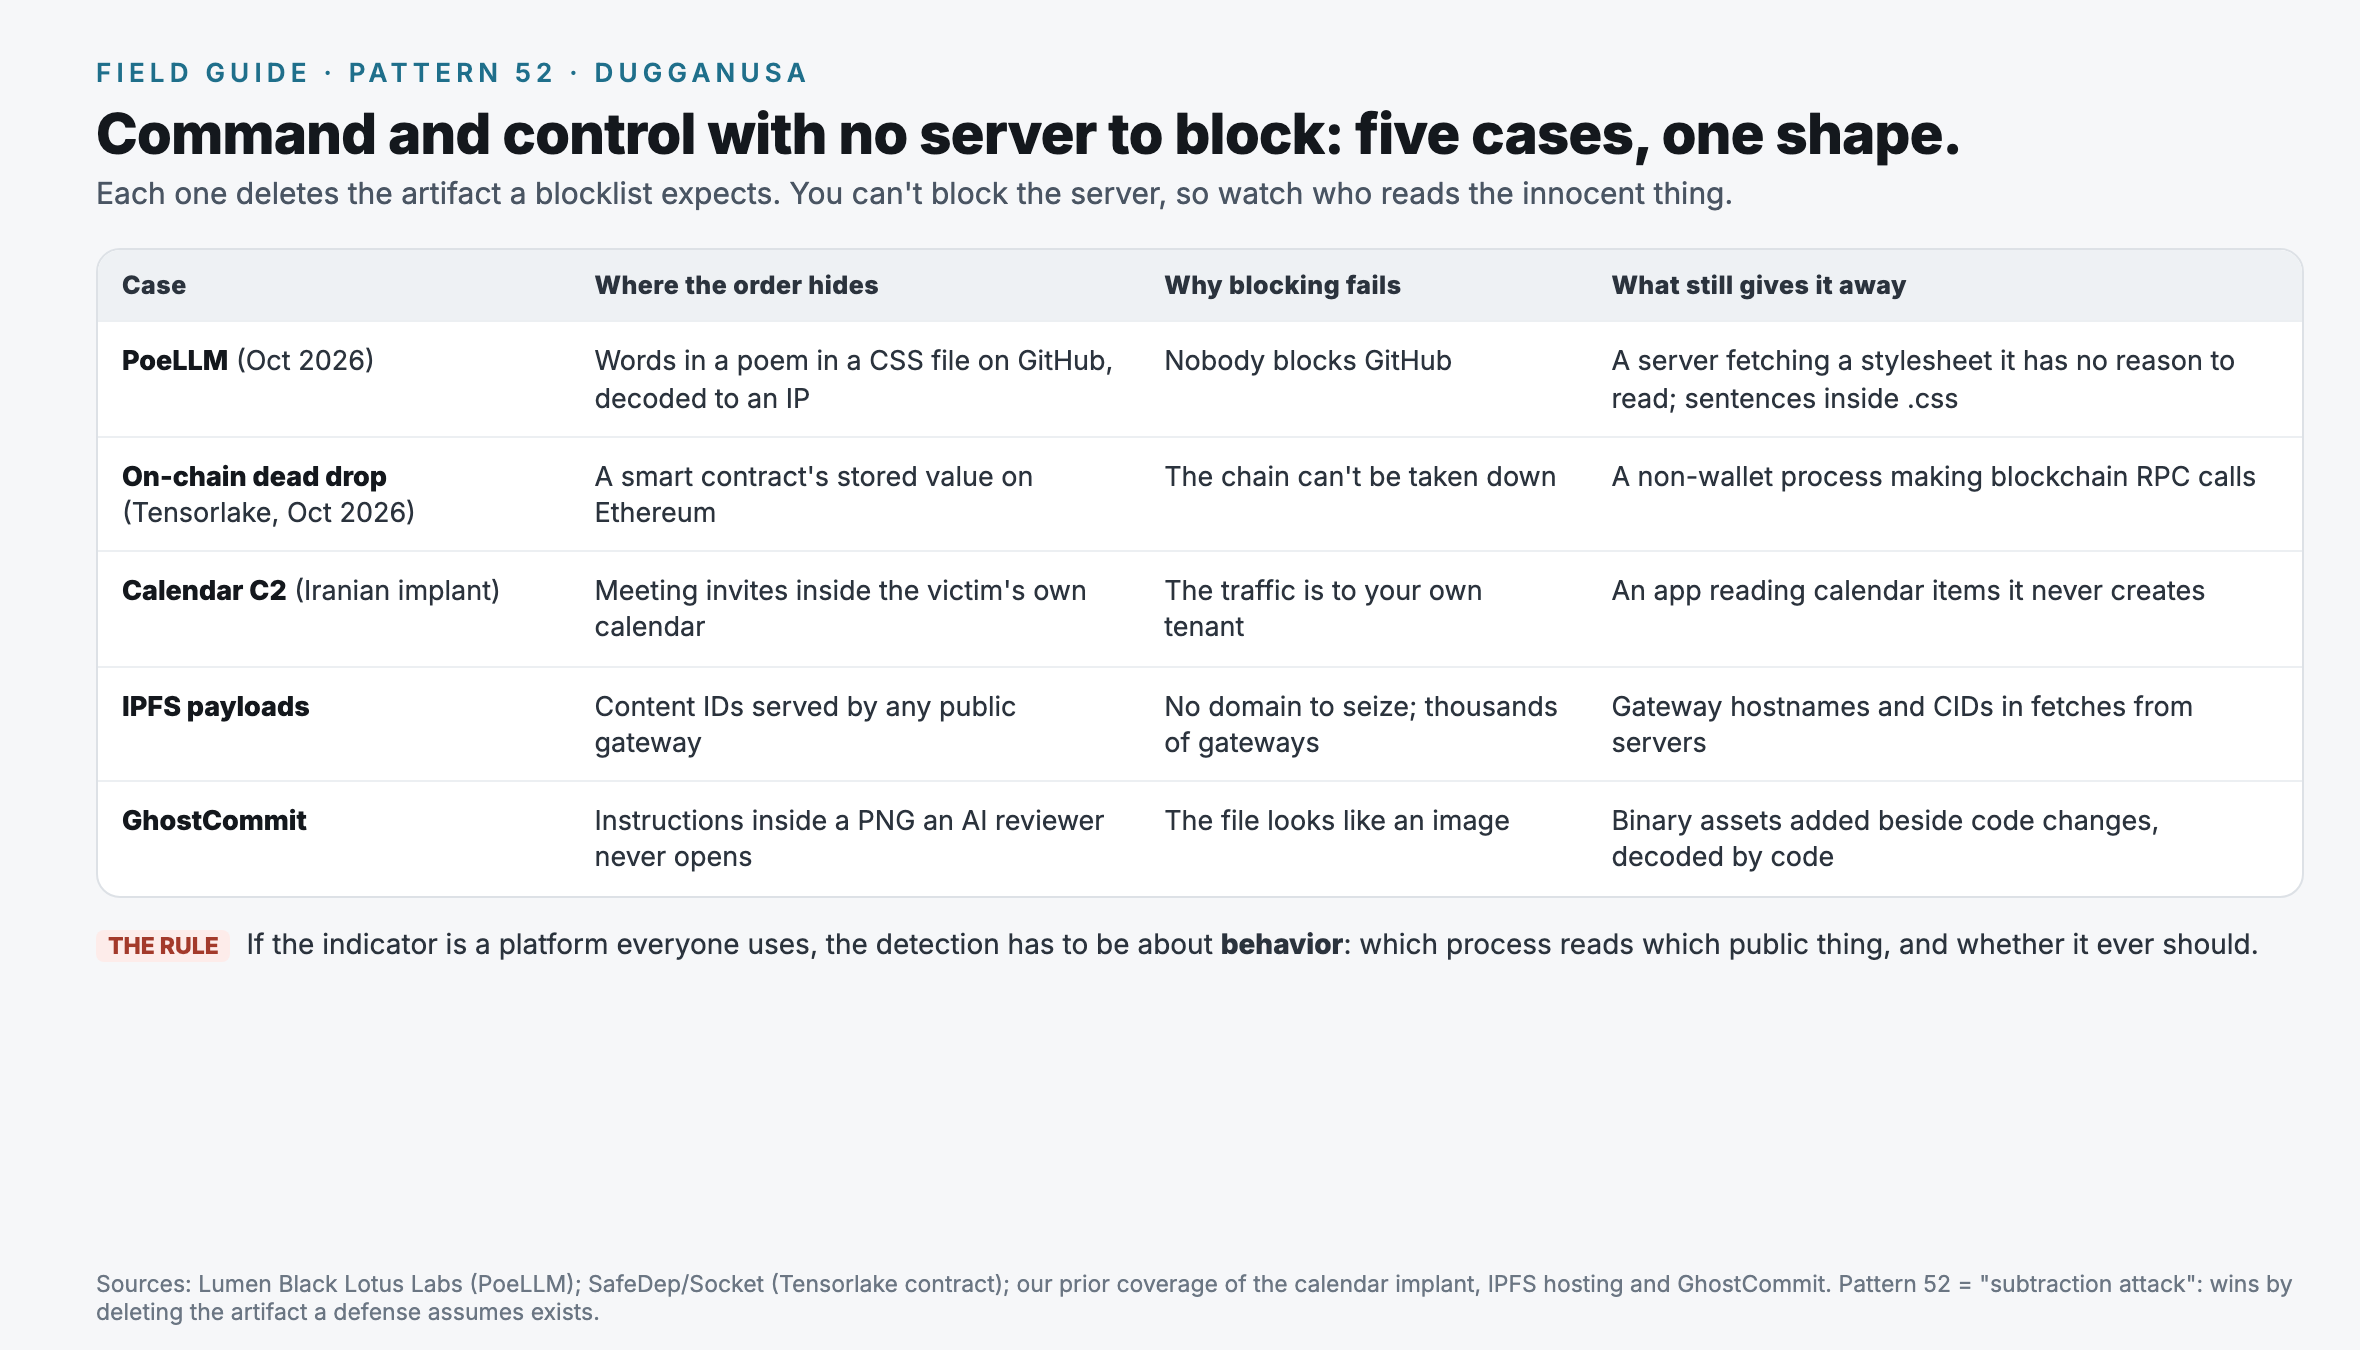
PoeLLM is not alone. When we ran it against our own archive by meaning rather than keywords, four more cases came back that we had written about separately. Put side by side, they are one pattern. We call it a subtraction attack, Pattern 52 in our catalog: the attacker wins by deleting the thing your defense assumes exists. Here, the thing they delete is the server.
The five cases
A poem on GitHub. PoeLLM, researched by Lumen's Black Lotus Labs, reads a poem from a CSS file in a GitHub repository and turns certain words into the four numbers of an IP address. Our write-up is here. The account that hosted the poem is now gone, which means the bots can no longer be redirected, but the operator only needs one new repository to start again.
A smart contract. Supply-chain worms in the Shai-Hulud family now read their next command address from a value stored in an Ethereum contract. The chain is public, permanent and impossible to take down, and updating the address costs the attacker a few cents. We covered the ChainDrop wave in August, and the Tensorlake package this morning used a new contract the same way.
Your own calendar. An Iranian implant took its orders from meeting invites in the victim's own mailbox. The traffic goes to your own email tenant. There is nothing to block that you are willing to block.
IPFS. Payloads hosted on the InterPlanetary File System are addressed by their content, not by a server, and served by thousands of public gateways. There is no domain to seize, and taking down one gateway changes nothing.
A PNG. GhostCommit hid instructions for an AI code reviewer inside an image file that the reviewer never opened. The file looked like an asset. The order rode along with the code.
What they have in common
Every one of these moves the order into something you trust and cannot block: a code host, a blockchain, your calendar, a content network, a file type. The attacker no longer needs a server that stays up. They need a public place where they can leave a note.
That changes the question a defender has to ask. "Is this address bad?" has no useful answer when the address is github.com. The question that still works is about behavior: which process on your machine reads which public thing, and should it ever?
How to catch them anyway
Watch readers, not destinations. A LiteLLM server has no reason to download a stylesheet from GitHub. A build agent has no reason to call an Ethereum node. An application that never creates calendar items has no reason to read them. Baseline which of your processes talk to which platforms, and alert on the first time a process reaches a platform it has never used.
Look for content in the wrong file type. Sentences inside a CSS file, a base64 blob inside an image, a long string in a contract read by something that is not a wallet. These look silly when you say them out loud, and they are cheap to scan for.
Hunt the shape, not the words. The poem is burned the moment it is reported. The habits around it are not: a fork of a popular repository, a throwaway account with a keyboard-mash name, a file the upstream project never had. This afternoon we hunted PoeLLM's shape instead of its poem. We found no second drop in the obvious place. But following the same idea on the servers it uses to deliver payloads turned up two command servers that were not in the original report. That is the method this guide argues for, and it worked on the first try.
Keep the blocklist anyway. The order may live on GitHub, but the payload still has to come from somewhere, and the miners still connect to a pool. Indicator feeds still catch the second hop. Ours carries all 20 PoeLLM indicators from Black Lotus plus the two siblings we found. Feeds stopped being enough. They did not stop being necessary.
The one-line version
If the indicator is a platform everyone uses, the detection has to be about behavior. Somebody always has to read the note. Watch who reads.
Was this useful? Rate this post. The widget is at the bottom of the page, and we read every response.
Every indicator in this post is in the feed. Free.
1.58M+ IOCs, STIX 2.1 / TAXII, 88% novel vs ThreatFox, exploited-CVE leads ahead of CISA. No credit card — a free API key in 30 seconds, and you can audit every claim above against the live endpoints.
Get your free key → analytics.dugganusa.com/stix/register
Was this useful? Thirty seconds, no cookies, no tracking, no third parties, your address hashed and never stored. If the box below does not load, the same question lives at https://analytics.dugganusa.com/nps.html?post=c2-with-no-server-to-block-field-guide-dead-drops-poem-blockchain-calendar-ipfs