A Seller Using the ShinyHunters Name Offers 335 Million Binance User Records for $900,000. Binance Says It Found No Breach and Calls It Likely a Scam. Nothing Is Verified. Here Is What to Do Anyway
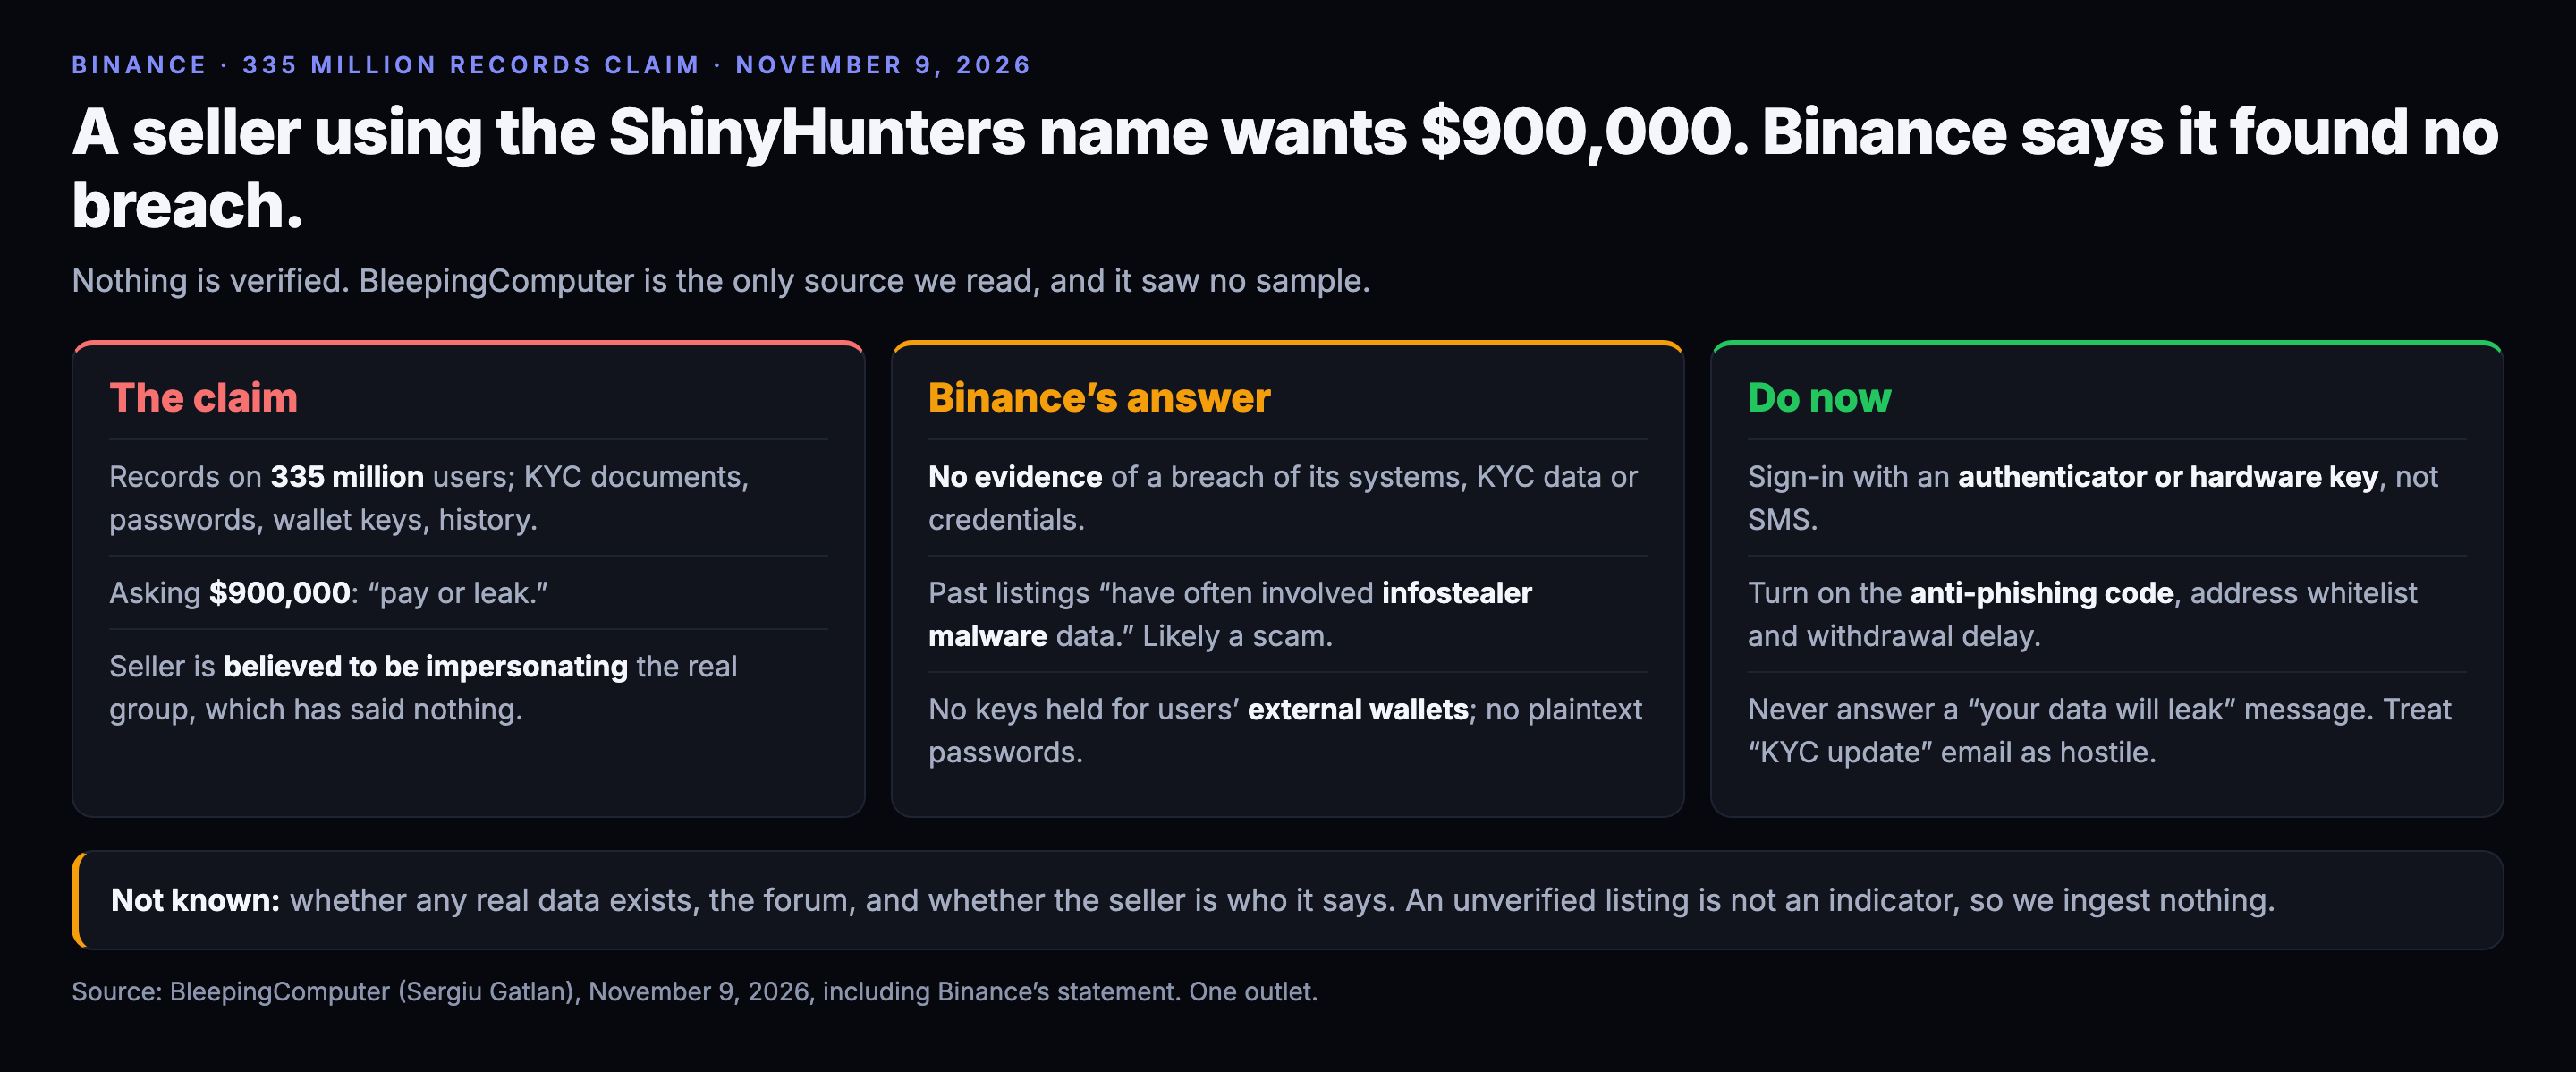
If you have a Binance account, do three things today whatever turns out to be true: check that sign-in uses an authenticator app or a hardware key rather than SMS, turn on the anti-phishing code for Binance email, and set a withdrawal address whitelist. A seller on a new underground forum, using the ShinyHunters name, says it holds records on 335 million Binance users and wants $900,000. Binance says it found no evidence of a breach and that the listing is likely a scam.
What has been reported
The only source is BleepingComputer's report of November 9, read for us by an agent. We have not seen the listing.
- The claim: a seller on "a newly emerged underground cybercrime forum" offers records on 335 million users for $900,000, listing KYC documents, internal infrastructure information, account passwords, wallet private keys, transaction history, emails and phone numbers. The seller wrote that Binance has "two options left: pay or leak."
- Who it is: BleepingComputer says the seller is believed to be impersonating the ShinyHunters extortion group, and reports no statement from the real group. It describes forum users doubting the listing.
- Binance's answer: a spokesperson said it found no evidence that Binance systems, customer KYC data or account credentials were compromised. It said similar past listings "have often involved infostealer malware data" and that this one is likely a scam. It also said it holds no private keys for users' external wallets and stores no plaintext passwords.
- Sample data: the report describes none, and says nothing was verified.
- Separate matter: the report mentions a separate, much larger Binance theft that we covered on October 30. This listing is not connected to it by any source we read.
What it means
Three outcomes are possible and the sources do not let us choose between them. The listing could be a scam by someone borrowing a feared name. It could be a collection of data from other places, such as malware that steals saved logins from users' own devices, which Binance itself suggests. Or it could be a real theft. Even in the harmless cases, the buyers and readers of such a post can use whatever fragments are real, so users should plan as if their phone number and email are in circulation. Nothing here shows keys or funds at risk through Binance's systems.
What to do
- Move Binance sign-in to an authenticator app or hardware key. Remove SMS as a second factor.
- Turn on the anti-phishing code, so legitimate Binance email carries a code only you know. Treat any email about a "breach", "KYC update" or "verify your account" as hostile by default.
- Turn on the withdrawal address whitelist and a withdrawal delay.
- Check your device for infostealers if you saved crypto logins in a browser. Change passwords from a clean device.
- Do not pay, reply to, or follow any message that says your data will be leaked unless you act. The seller's own line is a pressure tactic.
- Wallet seed phrases and private keys never go in an email, a form or a support chat. Binance says it does not hold keys for your external wallets, so any message asking for them is not from Binance.
What is not known
Whether any real data exists. What a sample would show. The forum, and whether the seller is the group it names. Whether the real ShinyHunters will comment. We add no indicators to our feed: none were published, and an unverified listing is not an indicator.
How we know, and how we checked
We read BleepingComputer's account of the listing and Binance's statement through an agent. This is one outlet and one statement from Binance. We did not look at the listing or any sample. Our earlier Binance posts cover the October theft and the iOS sandbox escape, not this listing.
Sources
BleepingComputer, "Binance denies data breach after alleged ShinyHunters claims," Sergiu Gatlan, November 9, 2026.
Every indicator in this post is in the feed. Free.
1.58M+ IOCs, STIX 2.1 / TAXII, 88% novel vs ThreatFox, exploited-CVE leads ahead of CISA. No credit card — a free API key in 30 seconds, and you can audit every claim above against the live endpoints.